Tenant isolation
Whether one financial customer can read or change another customer’s data, through the app or directly through the API.
Fintech and financial services
Under DORA, EU banks and insurers have to assess the ICT suppliers they rely on, and their supplier questionnaires usually ask for a recent independent pentest. I test the web app, API or mobile app they will use, and the report is written so their risk team can read it.
Assessment focus
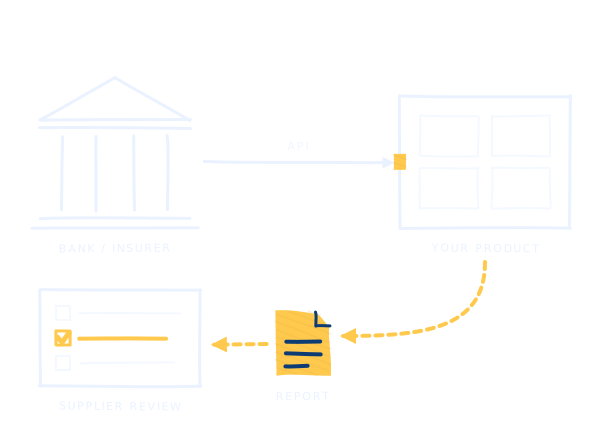
A bank usually reaches your product through an API and a handful of admin accounts on its side.
I start from what the bank or insurer can see and do in your product, then test whether another customer, or an attacker holding one of their accounts, can reach further.
Whether one financial customer can read or change another customer’s data, through the app or directly through the API.
How keys and clients are scoped and revoked, and what a leaked key would expose.
Payouts and limit changes followed end to end, looking for a step that can be skipped or replayed.
How far the product trusts the customer’s identity provider, and what each admin role on the customer side can do.
From a client
“Giuseppe was able to identify hard to exploit security issues that went undiscovered in the previous 3 pentests performed by 2 different providers.”
An example
A lending platform is onboarding an EU bank. The bank’s third-party risk team sends a questionnaire that asks about independent security testing of the API it will use.
The test is scoped around the API and the admin roles the bank will use, so the report answers the question the bank asked.
The test runs over about two weeks, with a draft report after the first.
Once the fixes ship, a retest confirms them, and the report you send the bank shows their status.
Deliverable
The report states the scope and dates of the test, then each finding and its retest status. Your customer can use it in its supplier due diligence under DORA, or under NIS2 when it is an essential or important entity. It does not certify compliance and it is not a threat-led penetration test (TLPT). Whether it meets their requirements is for your customer to decide.
Which systems and dates the test covered, so the bank can match it to the service it buys from you.
Each finding with its evidence and a severity rationale based on what was observed.
Retested fixes are recorded against the original findings, so the report you share stays current.
Common questions
No. DORA applies to the bank or insurer, and they decide what evidence they need from you. A recent independent pentest is evidence they commonly ask for in supplier due diligence.
No. TLPT is a threat-led test of the financial entity’s own critical functions, run by testers who meet DORA’s specific requirements for it. The test here is the application pentest a supplier is asked for.
Yes, in the same way. Essential and important entities have to manage security in their supply chain, so they ask their software suppliers for testing evidence.
DORA does not apply in the UK, but an EU bank that buys your software still has to assess you as an ICT supplier. Perspican is a UK company and works with suppliers on both sides.
Other services
Findings from scanners, AI tools or earlier assessments, checked one by one in your code. You learn which are real and how to fix them.
Short reviews between pentests: a sensitive change before release, or a fix that needs retesting.
When a verified fix requires production code, remediation engineering is available as a scoped add-on.
Send it with the product and the date the bank needs an answer by.
Prefer to write directly? [email protected]