Vulnerability reported, write-up pending
Security research
Vulnerabilities found and disclosed.
Alongside client work I look for vulnerabilities in open source software and router firmware, and report them to the maintainers. Each write-up explains how one flaw works and how it was fixed.
Write-ups
Findings so far.
Vulnerability reported, write-up pending
Vulnerability reported, write-up pending
Code of ethics
How the research is done.
Every finding here comes from a lab or a device I control and goes through coordinated disclosure with its maintainers.
Tested on what I own
Research runs on software in a lab I control and on devices I own. Systems and devices I do not own, or have no written permission to test, are never touched.
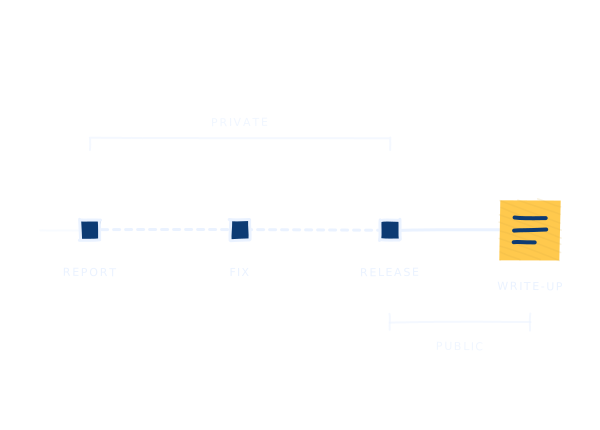
Reported privately
The maintainers hear about the flaw before anyone else. The timeline in each article shows when each step happened.
Published after the fix
A write-up waits for a fixed release, so there is an update to install by the time the details are public.
Enough to verify
Write-ups include what is needed to understand and reproduce the flaw on a test system. They do not include tooling that automates the attack.
These are the flaws I look for in a pentest.
Send the product and the deadline, and I will reply with a proposed scope.Related service: Penetration testing
Prefer to write directly? [email protected]