years building and scaling production software
Penetration testing and application security for software teams. Automation scales everything. Including risk.
Code now ships faster than anyone can review it.
A penetration test shows what an attacker can do with your apps, APIs, LLM agents and IoT devices. Each issue in the report comes with the evidence and a fix your engineers can apply.
The outside view
Tools look where your team points them.
Teams that test their own product with scanners or AI agents can catch a lot before it ships. Since they choose where to point those tools and which findings matter, security questionnaires and auditors often ask for a third-party test alongside that work.
Perspican tests with its own harness, refined over client engagements and vulnerability research, and does much of the work by hand. The testing draws on ten years of building and shipping products, so Perspican knows where to point the harness and what a fix costs a team with a release date.
Nothing goes into the report until it has been reproduced by hand, so your engineers spend their time on real issues. When a finding depends on a business rule, for example whether a trial account may export data, the report asks your team whether the behaviour was intended.
From a client
What three earlier pentests missed.
“Giuseppe was able to identify hard to exploit security issues that went undiscovered in the previous 3 pentests performed by 2 different providers.”
Why now
There is almost always a deadline.
- A customer's security questionnaire asks for a recent third-party penetration test
- A bank or insurer asks for testing evidence under DORA
- A release is going out and nobody has looked at it from the outside
- A new AI assistant or agent in the product can reach customer data
- An AI review or scanner returned hundreds of findings and nobody knows which ones matter
- An auditor wants evidence for ISO 27001 or SOC 2
- Investor due diligence has started
- Something happened, and you need to know what else is exposed
Services
Start with the problem in front of you.
Web, API & mobile penetration testing
A test of your web app, API or mobile app and the LLM features, cloud and connected IoT devices.
Finding validation
Findings from scanners, AI tools or earlier assessments, checked one by one in your code. You learn which are real and how to fix them.
Product security support
Short reviews between pentests: a sensitive change before release, or a fix that needs retesting.
When a verified fix requires production code, remediation engineering is available as a scoped add-on.
Who does the work
One tester for the whole engagement.
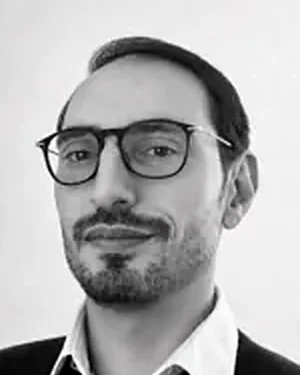
Giuseppe LobraicoOffensive security engineer
Every finding carries my name, and none is written up as more serious than it is.
vulnerabilities reported in 2026, 2 still in coordinated disclosureCVE-2026-110777
hands-on offensive security certification from OffSec
Send me what you need tested.
I usually reply within a working day with a proposed scope.
Prefer to write directly? [email protected]