One person throughout
I scope the work, carry out the testing and stay your contact until the retest. Nothing is passed to an undisclosed delivery team.
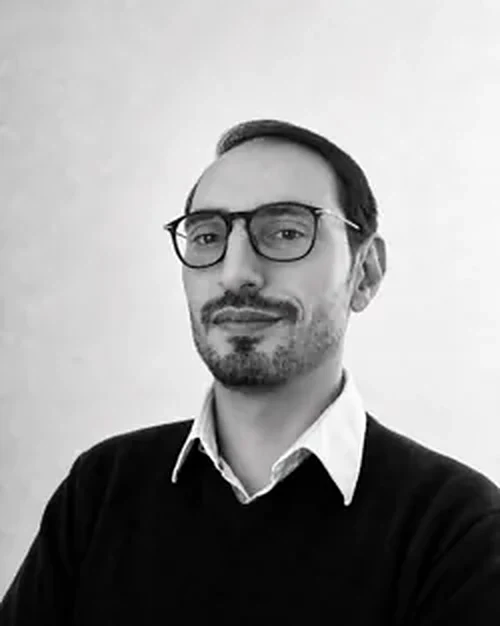
Perspican tests web applications, APIs and mobile apps, and validates findings from scanners and AI tools. Every engagement is scoped and delivered by Giuseppe Lobraico.
Background
I'm an offensive security engineer. For more than a decade I designed and ran production systems, and I now use that experience to find where they break.
Perspican is a trading name of Lobraico Ltd, an independent company operating since 2018, initially in software engineering. Before moving into security, I worked on Ruby on Rails and Go services, cloud and edge platforms, and the modernisation of Oracle legacy systems. The work ran in production for a fintech unicorn and for government agencies, as well as several startups, and for part of that time I led development teams as a tech lead.
Hacking has fascinated me since the early 2000s, when on IRC you learned by trying things out. Since 2025 it has been my full-time work, testing client applications and reporting vulnerabilities in third-party software, including open source projects and router firmware.
Security consultancies can also bring me in as a subcontractor or under their brand.
How I work
I scope the work, carry out the testing and stay your contact until the retest. Nothing is passed to an undisclosed delivery team.
Each finding is written up by the person who found it, and the same person runs the debrief.
What will be delivered, and when, is agreed in writing before the engagement starts.
Book a short call, or send the product and the deadline.
Prefer to write directly? [email protected]