Finding validation
Secure code review for scanner and AI findings.
I check the findings you already have against your code and tell you which ones are real. For each confirmed finding I suggest a fix.
- Input
- Findings and code
- Scanner, AI or earlier assessment output, with access to the codebase.
- Typical review
- Around 10 working days
- Effort depends on the volume of findings and on access.
- Deliverable
- One decision per finding
- With the evidence behind it.
The backlog
What happens to each finding.
Scanners and AI tools leave your team with a list of findings and no time to check them.
Many turn out to be false positives, because the input is never user-controlled or the behaviour is intended. I check each finding in the code, and in the running application where I can, and return it with a decision and the reason for it. Your engineers fix what is confirmed and close the rest.
Process and timing
The review works through the findings one at a time.
Around ten working days, confirmed once the findings and the codebase have been scoped.
- Scope the review
We look at where the findings come from, how many there are and whether I can run the application.
- Check each finding
For each finding I check whether attacker input can actually reach the code, and what an attacker would gain if it did.
- Record the decision
Each finding gets a decision and the evidence behind it. The confirmed ones also get a fix.
The deliverable
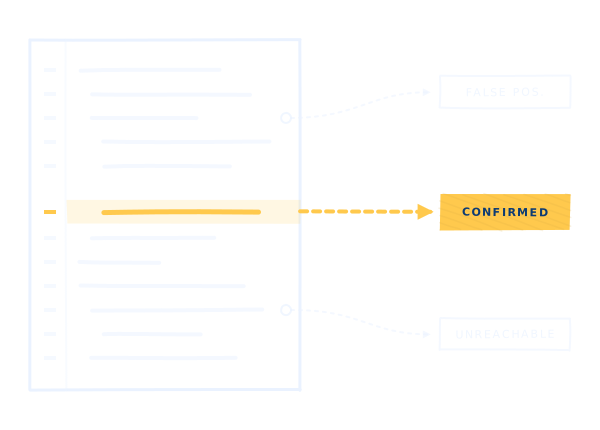
Every finding gets one of four decisions.
A prioritised list with a decision on every finding.
Each finding documents:
- Decision: confirmed, false positive, not reachable or needs more work
- Evidence for the decision, from the real code
- Exploitation conditions that have to hold for it to work
- Impact and priority for your product
- Fix, at the place in the code where the issue sits
If the same false positive keeps coming back, the report says which scanner rule or AI setting to change.
From a client
What three earlier pentests missed.
“Giuseppe was able to identify hard to exploit security issues that went undiscovered in the previous 3 pentests performed by 2 different providers.”
Common questions
Questions about the review.
What do you need to scope the review?
Where the findings come from and roughly how many there are, which repositories they cover, whether I can run the application and when you need the results.
How is the delivery date estimated?
Plan on around ten working days. I confirm the date once I have seen the findings and the codebase, because a large or complex backlog can change the effort a lot.
What decision does each finding receive?
Each finding is classified as confirmed, false positive, not reachable or requiring further work, based on the real code and application context.
What does the review deliver?
A prioritised list with a decision and evidence for every finding, and a fix for the confirmed ones. If the same false positive keeps coming back, the report also says which scanner rule or AI setting causes it.
Can you validate SAST, scanner and AI-generated findings?
Yes. Their output is where I start, and then I verify each finding by hand in the code.
Other services
Testing and ongoing support.
Web, API & mobile penetration testing
A test of your web app, API or mobile app, the cloud it runs on and any device that connects to it.
Product security support
Short reviews between pentests: a sensitive change before release, or a fix that needs retesting.
When a verified fix requires production code, remediation engineering is available as a scoped add-on.
Scoping starts from the findings you already have.
Tell me their source, approximate volume, stack and deadline.
Prefer to write directly? [email protected]