Applications and APIs
Whether one user or tenant can reach another’s data, and whether the business logic can be bent. OWASP ASVS and the API Security Top 10 are the checklist.
I test the paths an attacker would take, and spend most of the time on your product’s own rules, such as which tenant can see which data or who can approve a payment.
Perimeter
OWASP sets the baseline. From there I follow the product’s own entry points and integrations.
Clients usually need the report for an enterprise customer or for due diligence. It also works as technical evidence for ISO 27001, SOC 2 or PCI DSS, though the certification decision stays with the auditor.
Whether one user or tenant can reach another’s data, and whether the business logic can be bent. OWASP ASVS and the API Security Top 10 are the checklist.
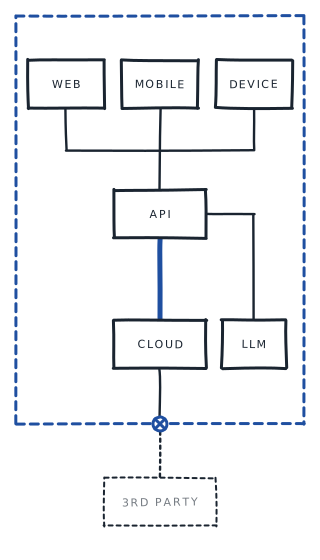
Exposed services and misconfigurations in the cloud the product runs on, and how far an attacker could escalate from them.
What iOS and Android apps store on the device and how they handle sessions, plus the APIs and external services they trust. The baseline is OWASP MASVS and MASTG.
Prompt injection, and what an assistant or agent can read or do through the tools and data it is given. The baseline is the OWASP Top 10 for LLM Applications.
When the product includes a connected device, what its firmware exposes and how the device authenticates to your API and cloud. The baseline is the OWASP Firmware Security Testing Methodology.
Process and timing
About two working weeks from agreed scope to final report and debrief. You get a draft after the first week.
Before testing starts we agree what is in scope, which test accounts I get and what must not be touched.
Automated tools cover the surface. I follow each promising lead by hand until it is either exploited or ruled out.
An executive summary for management, then each finding with its impact and the steps to reproduce it.
Once your fixes ship, I can test them again. The retest is booked separately.
The deliverable
Each finding shows where the issue sits in your code and how to fix it.
An executive summary covers exposure and priorities. Each finding documents:
From a client
“Giuseppe was able to identify hard to exploit security issues that went undiscovered in the previous 3 pentests performed by 2 different providers.”
Common questions
I need to know which applications and environments are in scope, what you want the test to answer, which roles and test accounts are available, what is off limits and when you need the report. From that we agree the authorised scope and the rules of engagement.
Yes, on request. The device’s web interface, its companion app and the APIs it talks to are tested as in any pentest, and the firmware is extracted and analysed when the scope allows it.
Yes, as part of the application pentest. The test covers what the model can read and which actions it can take for a user, including prompt injection through the documents or messages it processes and tool calls that skip the product’s permission checks.
Around two working weeks. I share a draft report after the first week, and the final report and debrief come at the end. The exact dates are set during scoping.
An executive summary, then the findings in order of priority. Each one has its impact, the evidence, the steps to reproduce it and how to fix it.
Not by default. A retest is optional and booked separately once your fixes are ready.
Yes, as technical evidence for customer assurance or for an ISO 27001, SOC 2 or PCI DSS programme. A pentest does not certify the organisation or guarantee compliance, and that decision stays with the auditor or the relevant authority.
I use automated harnesses and open-source models that run locally, to cover more ground and suggest what to try. I decide what to investigate and verify every finding myself before it goes into the report. Client data is never sent to an external AI service without your written approval.
Other services
Findings from scanners, AI tools or earlier assessments, checked one by one in your code. You learn which are real and how to fix them.
Short reviews between pentests: a sensitive change before release, or a fix that needs retesting.
When a verified fix requires production code, remediation engineering is available as a scoped add-on.
Assets, environments and dates are enough to start.
Prefer to write directly? [email protected]