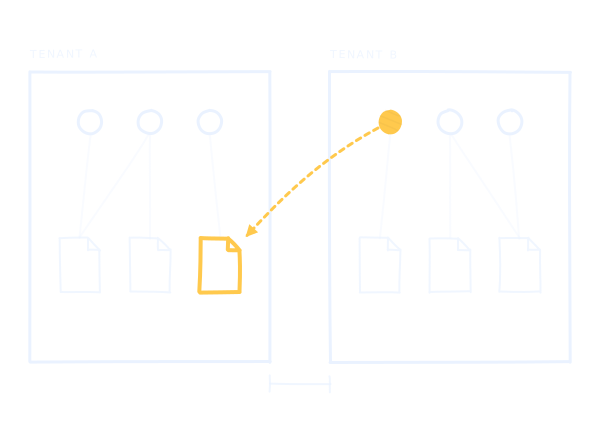
Roles and tenant boundaries
I compare what patients, practitioners, support staff and administrators can reach, looking for any path that reads or changes records from another account or customer organisation.
Healthtech
The pentest follows patient records through every role and customer organisation that can reach them, and each finding has evidence your engineers can reproduce.
Assessment focus
A healthtech product often shows the same patient record to several roles, and to more than one customer organisation.
I map each role to the actions it is allowed to take, then test those actions with direct requests to the API and through complete workflows such as invitations and exports.
I compare what patients, practitioners, support staff and administrators can reach, looking for any path that reads or changes records from another account or customer organisation.
I run workflows such as referrals and consent changes end to end, looking for a step that skips a permission check.
I test object-level authorisation and session handling on web, API and mobile clients, and how far the product trusts its identity provider and connected services.
I follow attachments and exported reports from upload to sharing, looking for predictable file references and links that never expire.
“I've worked with Perspican to identify the security gaps in three different applications storing medical data. Giuseppe was able to identify hard to exploit security issues that went undiscovered in the previous 3 pentests performed by 2 different providers.
He understands deeply secure software engineering best practices, and I was really impressed by his ability to identify the issue in the codebase and precisely suggest the solutions to the problem.
I'd recommend his services to any business that handles sensitive data”
An example
A practitioner works for two clinics on the same platform. One clinic removes them, while their account stays active for the other.
I create test accounts in both clinics, with one practitioner who belongs to each of them.
The first clinic removes the practitioner. I then send every request they could make before, through the app and directly to the API.
A file endpoint still returns the first clinic’s attachments. The finding names the endpoint and the records exposed, with the steps to reproduce it.
Deliverable
Each finding names the role and the records involved, with the steps to reproduce it. I walk your team through the report, and agreed retests are recorded against the original findings. The report can also serve as technical evidence for the NHS DSPT, a DTAC assessment or a HIPAA risk analysis, while compliance decisions stay with the assessor.
Numbered steps from a stated account state, with the requests and responses that show the behaviour.
The records or actions exposed and the tenants involved, with a severity rationale based on what was observed.
A fix, and the retest status once it ships. Similar code paths worth checking are listed too.
Common questions
No. The test runs on test accounts with synthetic records, ideally in a staging environment that matches production. If part of the test has to run in production, we agree in writing which accounts and records it may touch.
The product’s side of them is. I test how far the product trusts the tokens and webhooks it receives from connected services. The third-party systems themselves stay out of scope unless their owner authorises the test in writing.
Yes, as technical evidence of what was tested and found. The compliance decision stays with the assessor.
Usually 8 to 12 consultant days, depending on how many roles and apps are in scope. The fixed fee and the dates are set after scoping.
Other services
Findings from scanners, AI tools or earlier assessments, checked one by one in your code. You learn which are real and how to fix them.
Short reviews between pentests: a sensitive change before release, or a fix that needs retesting.
When a verified fix requires production code, remediation engineering is available as a scoped add-on.
Send the product and its user roles, with the date you would like the test to start.
Prefer to write directly? [email protected]